Life Sciences Software, AI & Regulatory Services
Regulatory, Quality, Software & AI Expertise — for Medical Devices, IVDs, Pharma & Biotech
With 30 years in the life sciences, across pharma, medical devices, IVDs and combination products, we support organisations at every scale: auditing and training global manufacturers, guiding new-start companies through their first QMS, and supporting software and AI development under EU MDR, EU IVDR, GMP, the EU AI Act, and international ISO and IEC standards.
Four Ways We Support Your Device
From a first QMS to an AI-enabled device in clinical use, we help medical device organisations get compliant, build safely and train their teams.
Regulatory, Quality & Development Services
Regulatory strategy, QMS, technical documentation, cybersecurity, software development and auditing.
AI Validation
Validation of the AI used in your quality and regulatory workflows, using our Oversure™ framework.
Training
Programmes for industry teams, plus free e-learning courses.
Toolkit
Ready-made QMS, software and cybersecurity packs, and AI-enabled compliance tools.
Written by People Who Help Write the Standards
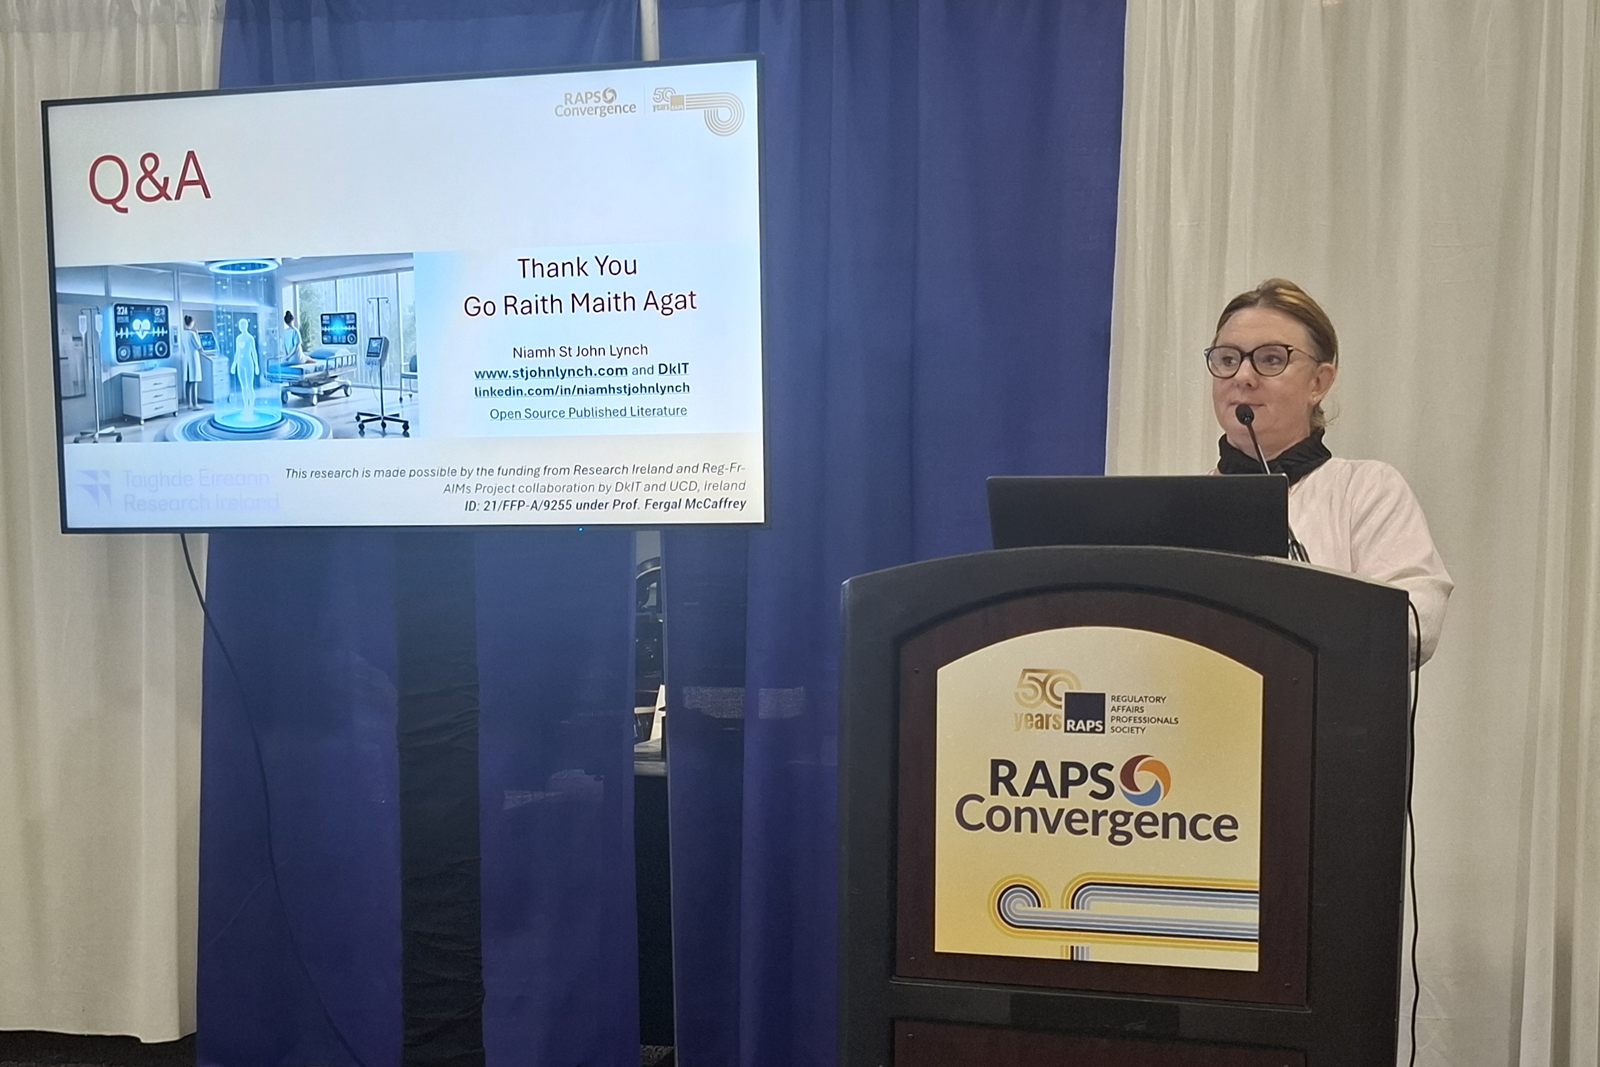
Our work draws on active participation in IEC TC62, NSAI and CEN-CENELEC committees, four years of Notified Body assessment experience, and doctoral research into regulatory frameworks and governance for AI-enabled medical devices.
Let's Talk About Your Device
Whether you are preparing for an MDR audit, building a first QMS, or developing an AI-enabled medical device, we welcome a conversation about how we can help.
Research Output
All publications are archived in the DkIT STÓR repository. Journal articles, book chapters, conference papers, a research artefact, and teaching resources.
Doctoral Research: Investigating AI-enabled medical device regulatory change management — examining how manufacturers, notified bodies, and competent authorities navigate post-market obligations under EU MDR 2017/745 and the EU AI Act (Regulation 2024/1689) when AI model updates occur in deployed devices. PhD with DkIT, registered under DCU, as part of the DkIT/UCD Collaborative Project on Trustworthy AI-enabled Medical Devices.
Selected Figures from Published Work
Illustrative diagrams drawn from peer-reviewed publications. Click the source links to access the full papers in DkIT STÓR.
AIeMD Standards Landscape: Regulatory & Technical Layers
Adapted from: St John Lynch et al. (2024) Artificial Intelligence-Enabled Medical Device Standards: A Multidisciplinary Literature Review. EuroSPI’24, Munich. View on Springer
Active Projects
AI Change Management Process Assessment (ChangeIQ)
Development of a structured AI-enabled web application for regulatory change management assessment for medical device manufacturers. Based on a 19-section, ~160-question framework spanning EU MDR 2017/745, EU AI Act, ISO 13485:2016, IEC 62304, and ISO 14971. Formally archived as a research artefact in DkIT STÓR.
EU Simplification Package: MDR/IVDR & AI Act Alignment
Analysis of the EC's Simplification Digital Package and Omnibus Proposal and their implications for AI-enabled medical device manufacturers. Presented at the Irish MedTech QA/RA Regulatory Forum (Limerick, March 2026); published in Journal of Medical Device Regulations (in press, 2026).
Trustworthy AI Framework for Healthcare
Proposed framework for trustworthy AI in healthcare, developed through multidisciplinary research. Published as a Springer Nature book chapter (CCIS, 2025) and presented at EuroSPI'25 (Riga) and AICS 2025 (DCU, Dublin).
AI Standards Gap Analysis — MDR & AI Act
Systematic identification of gaps between existing harmonised medical device standards and EU AI Act Annex I requirements for high-risk AI systems. Underpins contributions to CEN-CENELEC AI Task Groups 1 and 2 and IEC TC62 expert committee work.
International & European Standardisation
Contributing to standards development at national, European, and international levels, with a focus on medical device software, AI governance, and regulatory alignment of emerging AI standards with EU MDR and the AI Act.
WG 17
Plenary
JWG 12
JWG 15
PT 63450
PT 63621
SC 62A
AI TG1
AI TG2
ETC/TC10
IEC 62304:2006+AMD1:2015
Medical device software lifecycle processes. Central to change management analysis for AI-enabled medical devices and the ChangeIQ assessment framework.
ISO 14971:2019
Risk management for medical devices. Core framework for AI-related hazard identification and risk control measures.
ISO 13485:2016
Medical devices quality management systems. Anchors change control procedures and post-market surveillance obligations for AIeMD manufacturers.
ISO 42001:2023
AI management system requirements. Analysed for alignment and gap against EU AI Act Annex I within CEN-CENELEC TG work.
IEC PAS 63621
Guidance on artificial intelligence for healthcare. Key bridge standard under review in TC62 context and referenced in the literature review (EuroSPI'24).
BS 30440:2023
Change management for AI systems. Referenced in the AI Change Management Process Assessment artefact and ChangeIQ tool development alongside EU AI Act obligations.
The Road to Market
Seven Stages from Concept to CE Mark — and Beyond
However a device looks from the inside, it travels the same seven-stage road under EU MDR — classification, quality management, technical documentation, clinical evidence, conformity assessment, CE marking, and post-market surveillance. What changes with risk class is how much evidence each stage needs, not the shape of the journey. This is the map I walk clients through from their very first conversation.
Seven Stages, One Predictable Road
Every device — Class I to Class III, hardware or software, legacy or AI-enabled — follows the same seven-stage route to market. The map below is the same one I use with clients on day one.
From Concept to CE Mark
Each stage builds on the last. Skipping ahead — starting technical documentation before classification is settled, for example — is the most common cause of rework later.
The Road Doesn't Change — the Traffic Does
Risk classification doesn't add or remove stages — it changes how much scrutiny each one gets.
Lighter Traffic
Non-sterile, non-measuring Class I devices can self-declare conformity — no Notified Body involvement — but the QMS, technical file, and post-market obligations still apply in full.
Heavier Traffic
Notified Body review deepens with risk — from sampling technical documentation at Class IIa to full quality system and design dossier scrutiny at Class III — and clinical evidence expectations rise to match.
Walking This Road, Together
Whether you're mapping this journey for the first time or you're deep into technical documentation and need a second pair of eyes, I help medical device organisations move through each stage with confidence.
Services for MedTech
& Life Sciences
Consulting · Auditing · Development · AI · Training
From a first QMS to a global submission, we help medical device and life sciences organisations get compliant, build safely and train their teams. We combine 30 years of regulatory and quality experience with hands-on software engineering and applied AI, and with active roles in the standards committees where the rules are written.
Find the Service You Need
Plan your route to market, build the software and AI behind your device, validate and audit it, and train your team. Each service has its own page with the detail.
Regulatory Strategy
Classification, pathways and evidence for the EU, UK, US and beyond.
Learn more →AI Change Management
Guide AI projects from first idea to live operation, in your organisation and in your devices.
Learn more →Software Development
Medical device software, SaMD and AI-enabled devices built to IEC 62304, with stage gates and design controls.
Learn more →Usability Engineering
Use-risk analysis, formative and summative studies, and a free template.
Learn more →
Expertise Where It Matters
St John Lynch & Co brings together significant life sciences and regulatory experience, working with a network of independent specialists where a project needs them. That depth spans regulatory affairs, clinical strategy, software and systems engineering, and applied AI — bringing genuine technical fluency to every engagement.
What We Offer
The full range of what we do, grouped by how we work with you. Every engagement draws on current regulatory practice, active standards participation and ongoing doctoral research, so advice reflects the latest developments in EU MDR, the AI Act and international standards.
Medical Device Regulatory Strategy
Strategic guidance and regulatory reviews for manufacturers navigating conformity pathways across the EU, UK, and US — with growing reach into Japan, Australia, Brazil, and Canada. Particular expertise in EU MDR 2017/745 and the implications of the EC's Simplification Digital Package and Omnibus Proposal for AI-enabled medical devices.
AI-Enabled Medical Device Compliance
End-to-end compliance support for AI-enabled and adaptive medical devices — covering Article 22 obligations under the EU AI Act (Regulation 2024/1689), post-market change management, and PMCF strategy.
Standards Gap Analysis & Implementation
Practical gap analysis against IEC 62304, ISO 14971, ISO 42001, IEC PAS 63621, and BS 30440:2023 — informed by active participation in the committees developing these standards.
Quality Management Systems
QMS review, design, optimisation, and independent quality reviews for medical device manufacturers under ISO 13485, with specialist focus on change control, AI model update governance, and software development under IEC 62304.
Contract QMS for Fast-Track Compliance
A hosted, ready-to-operate quality management system for organisations that need one fast rather than build one from scratch — new-start medical device companies getting up and running quickly, and health institutions manufacturing devices in-house under Article 5(5) of EU MDR/IVDR.
AI Change Management Frameworks
Change assessments and AI change management process design — including adaptation of the ChangeIQ framework for organisational contexts and integration with existing regulatory change control procedures.
Technical Documentation
Preparation of compliant technical documentation for regulatory submissions — including clinical evaluation reports, risk management files, and conformity assessment materials for AI-enabled and software-as-a-medical-device (SaMD) products. Can extend to submission compilation and direct communication with notified bodies or competent authorities where required.
AI Process Integration
Practical support embedding AI tools and workflows into existing quality and regulatory processes — from pilot to validated, audit-ready operation, without disrupting what already works.
Market Access Strategy
Regulatory strategy for entering new markets — EU, UK, US, and beyond — including classification, conformity route selection, and coordination across jurisdictions for multi-market launches.
Clinical Evaluation & Post-Market Surveillance
Clinical evaluation plans and reports, post-market surveillance plans and reports, and PMCF plans and reporting — the full clinical evidence lifecycle required under EU MDR Annex XIV.
Contract QMS for Health Institution App Developers
A hosted, ready-to-operate quality management system tailored for health institutions building and testing their own software applications in-house under Article 5(5) of EU MDR/IVDR.
Medical Device Cybersecurity as a Service
Security risk management, secure product lifecycle implementation, and security-driven change management for connected and software-based medical devices — aligned with IEC 81001-5-1, EU MDR Annex I cybersecurity requirements, and FDA premarket cybersecurity guidance.
Quality & Regulatory Auditing. Independent QMS, supplier, software lifecycle and technical documentation audits against ISO 13485, FDA QMSR, EU MDR/IVDR, ISO/IEC 27001 and the IEC software and cybersecurity standards, drawing on experience as a former Notified Body technical reviewer and site auditor.
Health Software Development
Development of health software and wellness applications, including products built to IEC 82304-1 and IEC 62366-1 usability engineering, and aligned with the emerging IEC 62366-3 for AI-enabled devices, with a clear eye on the regulatory boundary — helping teams build features and evidence that hold up if a product later needs to cross into SaMD territory.
SaMD Development
Hands-on development support for Software as a Medical Device — architecture, lifecycle documentation, and verification activities built to IEC 62304 from the outset, not retrofitted after the fact.
Medical Device Risk Management
Risk management file development and review, hazard analysis, and benefit-risk determination under ISO 14971 — including risk considerations specific to AI-enabled devices. Complemented by AskRiskie, an AI-enabled risk management tool built for lifesciences compliance.
Usability Engineering
Specialist support for usability engineering programmes across the IEC 62366 series — covering formative and summative evaluation under IEC 62366-1, practical implementation guidance per IEC 62366-2, and compliance strategy aligned with the emerging IEC 62366-3 requirements specific to AI-enabled medical devices.
Change Governance Maturity Assessment
A free, publicly accessible tool from St John Lynch & Co — designed to help medical device manufacturers and regulated organisations quickly benchmark their current maturity in change governance, including for AI-enabled systems.
How mature is your change governance?
This structured assessment tool walks through key dimensions of change governance for AI-enabled systems, aligned with EU MDR, the EU AI Act, and relevant international standards. Use it to identify gaps, prioritise improvement areas, and build a baseline before engaging a consultant or auditor.
Why Work With Me
My consulting practice is distinctive because it is rooted simultaneously in active research, international standards development, and over two decades of hands-on industry practice.
As a doctoral researcher investigating AI-enabled medical device regulatory change management, an IEC TC62 expert member contributing to the very standards your organisation must comply with, and a practitioner with 30+ years in the life sciences, I offer a rare combination of current academic insight, standards intelligence, and practical regulatory experience.
That experience includes a career as a Notified Body technical reviewer and site auditor, assessing manufacturers' technical documentation and quality management systems against EU regulatory requirements — giving me direct insight into how conformity assessments are conducted and what assessors look for. I have worked with leading global medical device organisations including Boston Scientific, Johnson & Johnson, Abbott, Medtronic, Veryan, Mylan, and others, across a broad range of device types and regulatory submissions.
The Assessor's Perspective
As a former Notified Body technical reviewer and site auditor, I have assessed technical documentation and QMS compliance from the other side of the table. This gives consulting clients a rare advantage: advice shaped by direct knowledge of how conformity assessments are conducted and what reviewers scrutinise.
Insider View of Emerging Standards
As an active participant in IEC TC62, NSAI/ETC/TC10, and CEN-CENELEC AI Task Groups 1 & 2, I work on the standards your organisation will need to comply with — often before they are published. This means consulting guidance informed by where standards are going as well as where they are today.
Academic Rigour in Applied Contexts
My doctoral research on AI-enabled medical device regulatory change management directly informs consulting engagements, ensuring advice is anchored in peer-reviewed evidence, systematic literature analysis, and current regulatory intelligence.
Regulatory Science Meets Software and AI
Few practitioners combine deep expertise in medical device regulation (MDR, ISO 13485, IEC 62304, ISO 14971) with the emerging AI governance landscape (EU AI Act, ISO 42001, BS 30440:2023) and hands-on software and systems engineering. I bridge all three, so advice on SaMD and AI-enabled devices reflects how the software is actually built.
Ireland, EU, and International Reach
Based in Ireland and representing Ireland at IEC and NSAI, I provide specialist support for organisations operating in or entering the Irish and broader EU medical device market, with understanding of both local and European regulatory contexts.
Key Frameworks & Standards
Consulting engagements draw on expertise across the following regulatory frameworks and standards — all areas of active research and standardisation participation.
2017/745
2024/1689
Ed.2 (dev.)
2019
2023
2016
Ready to Discuss Your Regulatory Challenges?
Whether you are preparing for an MDR audit, navigating AI Act obligations for a software medical device, or building an AI governance framework, we welcome a conversation about how we can support your organisation.
Independent Auditing
for MedTech
ISO 13485 · FDA QMSR · IEC 62304 · IEC 82304-1 · IEC 81001-5-1 · ISO 27001 · EU MDR · IVDR
Our audits draw on four years as a Notified Body technical reviewer and site auditor, IRCA-certified Lead Auditor training in ISO 9001 and ISO 13485, and 30 years across quality, regulatory, software and security. We audit quality systems, software lifecycles, suppliers and technical documentation against the standards and regulations your devices are built to.
Eight Standards and Regulations, One Audit Team
Most medical device organisations are audited against several frameworks at once. We can audit against each, or combine them in a single programme so your teams are not interviewed three times for the same process.
ISO 13485:2016
Internal audit programmes, certification-readiness audits and process audits of your quality management system.
FDA QMSR
Gap and readiness audits against the Quality Management System Regulation (21 CFR Part 820), which incorporates ISO 13485 and has applied since 2 February 2026.
EU MDR 2017/745
Conformity gap and readiness audits of your QMS and technical documentation against MDR requirements, including software and AI-enabled devices.
EU IVDR 2017/746
Gap and readiness audits for IVD manufacturers, covering performance evaluation, technical documentation and post-market obligations.
IEC 62304
Audits of your software development and maintenance processes, safety classification, SOUP management and lifecycle records.
IEC 82304-1
Audits of health software product requirements, validation and the product-level safety and security evidence behind them.
IEC 81001-5-1
Audits of your secure product development lifecycle, including threat modelling, SBOM management and vulnerability handling.
ISO/IEC 27001
Audits of information security management systems for organisations that develop or host health software and handle sensitive data.
Matched to What You Need Next
The right audit depends on whether you are keeping a certificate, qualifying a supplier or preparing for a first assessment.
Internal Audit Programmes
An annual internal audit plan covering your processes, run by an independent auditor with the technical depth to challenge software, risk and design records.
Supplier Qualification Audits
On-site or remote audits of critical suppliers, including software and cloud service providers, with findings you can act on and defend.
Pre-Certification Readiness Audits
A realistic rehearsal of a Notified Body or regulator audit, with a clear list of findings ranked by severity and a plan to close them.
Technical Documentation Reviews
Structured reviews of your technical file for coverage, consistency and traceability, from intended purpose through risk management, verification and clinical evidence.
Impartial by Design
Our audits are consultancy audits that prepare you for certification. Certificates themselves are issued only by Notified Bodies and certification bodies. We keep our audit work and any advisory work for the same client clearly separated, so you always know which role we are in.
Planning an Audit?
Tell us which standards apply, how many sites or suppliers are involved and when you need a report, and we will propose a scope and schedule.
Usability Engineering
for Medical Devices & Health Software
IEC 62366-1 · ISO 14971 · EU MDR · FDA Human Factors
Use errors cause real harm, and regulators expect evidence that your users can operate your device safely. We plan and run usability engineering for software medical devices, health software and AI-enabled devices, from use specification and use-risk analysis through formative studies to summative evaluation and the usability engineering file.
From Use Specification to Summative Evaluation
IEC 62366-1 asks for a documented usability engineering process that runs alongside design and risk management. We support each step and keep the records consistent with your technical documentation.
Use Specification
Intended users, use environments, patient population and the frequently used and safety-related functions of your software.
Use-Risk Analysis
Task analysis, use errors, hazardous situations and risk controls, feeding the risk management file and the list of hazard-related use scenarios.
Formative Evaluation
Design reviews, walkthroughs and early user studies on wireframes, prototypes and builds, with findings fed back into the design.
Summative Evaluation
A protocol-driven study with representative users, analysis of every use error and close call, and a usability engineering file ready for review.
Watching Real Users Use Your Software
We design and run usability studies for software medical devices and health software: protocols, participant profiles, simulated-use scenarios, observation and analysis. Every finding links back to your use-risk analysis, so the evidence reads as one story.
Formative Studies
Small, fast sessions on sketches, wireframes and prototypes that find problems before they reach code.
Summative Studies
Simulated-use studies with representative users to show that the hazard-related use scenarios are managed.
Flexible Delivery
Moderated sessions on-site or remotely, with the observation, recording and analysis set up around your device and users.
Where Software Use Errors Start
Software introduces use risks that hardware devices rarely face. We review interfaces for the patterns that most often lead to harm and design controls that work in practice.
Data Entry & Units
Dose, weight and measurement entry, default values, units and range checks.
Alerts & Decision Support
Alarm and alert design, information hierarchy and the risk of alert fatigue.
Onboarding & Instructions
First-use flows, in-app instructions for use and safety messages people actually read.
AI-Enabled Devices
How users interpret AI outputs, over-reliance on recommendations and effective human oversight, aligned with the emerging IEC 62366-3.
Free Whitepaper: IEC TS 62366-3 for AI-Enabled Devices. Our practical guide to the first Committee Draft of IEC TS 62366-3, with a fully worked example, guidance for generative AI and AI agents, and methods that find the risks a single-user analysis can miss.
Use-Risk Analysis Template
A ready-to-use Excel workbook for use-related risk analysis, aligned to IEC 62366-1 and ISO 14971. It includes a Use Specification sheet, a Use-Risk Analysis that calculates risk before and after control, a hazard-related use scenario summary for summative planning, and editable severity and probability scales with a risk matrix. Three worked examples for a medication dose calculator app show the level of detail expected.
Our Usability Engineering SOP is also part of the QMS SOPs & Templates pack in the .
Planning a Usability Study?
Tell us about your device, your users and your timeline, and we will propose a usability engineering plan that fits your design and regulatory schedule.
Medical Device Software
Development
SaMD · SiMD · AI-Enabled Devices · IEC 62304 · IEC 81001-5-1 · EU AI Act
We design, build and verify health software and software medical devices, with design controls, risk management, cybersecurity and documentation built in at every stage. Our secure development lifecycle follows IEC 81001-5-1, and every phase ends at a documented stage gate, so your technical documentation grows with the product.
Development Built for Regulated Products
Whether you are starting from a concept or already have code, we work at the level your product needs, under your QMS or ours.
Full Product Development
We take your device from intended use to a released, documented product, ready for your Notified Body or FDA submission.
Development Partner
Our engineers work with your team to build reliable, safe software that meets regulatory requirements, within your own lifecycle and tools.
Process & Tooling
Software development plans, SOPs, traceability and CI/CD set up so that compliance is a by-product of how your team already works.
Remediation
Gap assessment and remediation of legacy software or software of unknown provenance where required, including updates for new standards such as IEC 62304 Edition 2.
Phases, Stage Gates & Design Controls
Our software development lifecycle follows IEC 62304 and ISO/IEC 12207 and maps every phase to the design control requirements of ISO 13485 and the FDA QMSR. For AI-enabled devices, an AI lifecycle track runs alongside the same phases. Agile teams work inside this framework: sprints happen within phases, and the gates are where the evidence comes together.
Swipe sideways to see the full lifecycle →
What Must Be True Before a Phase Closes
Each gate is a formal design review with Development, Quality and Regulatory. Nothing moves forward on a promise to document it later.
Plan Approved
Software development plan approved, safety class or rigor level assigned with rationale, and AI planning complete where AI is present.
Requirements Baselined
Functional, performance, security, usability, safety and AI requirements reviewed and baselined, with traceability started.
Architecture Approved
Every software item identified and classified, SOUP listed, and security trust boundaries documented for threat modelling.
Design Approved
Unit-level design reviewed before coding, with security requirements and input validation mapped to the design.
Code Verified
Independent code review, static security analysis on every build, and unit tests passed with no open critical defects.
Integration Verified
All interfaces tested, including error conditions, with defects resolved or risk-accepted and the report approved.
System Verified & Validated
System, security and usability testing complete, AI performance and bias testing passed, and no open critical or high defects.
Release Approved
Release record signed by Quality, Regulatory and Product Security, SBOM current, known anomalies justified, and post-market monitoring active.
AI-Enabled Devices, Built to Be Trusted
AI brings risks that conventional software does not: data dependency, bias, drift and opacity. Our AI lifecycle adds the controls regulators now expect under the EU AI Act, the IEC 62304 Edition 2 AI Annex and the FDA's AI guidance, inside the same stage gates.
Performance Criteria First
Clinically meaningful acceptance criteria, subgroup requirements and human oversight design are fixed before any model is trained.
Data Governance
Documented data sources, annotation, representativeness and bias assessment, with a test set locked away from development.
Robustness & Bias Testing
Subgroup analysis, out-of-distribution and adversarial testing, and clinical validation matched to your device class.
Model Cards & Oversight
Model cards, output explanations and override mechanisms that let clinicians use AI outputs appropriately.
Drift Monitoring & PCCP
Performance and drift monitoring with defined triggers, and predetermined change control plans for planned model updates.
AI Threat Modelling
STRIDE-AI analysis of data pipelines, model weights and inference, including data poisoning and adversarial inputs.
Evaluating Pre-Trained Models Before You Build on Them
Pre-trained and foundation models are software of unknown provenance. Before one goes into a medical device, we evaluate its training data provenance, licence, performance in your intended use, bias, security and vendor support. Our method comes from our own peer-reviewed research, which led directly to IEC 63767, the new international standard for evaluating pre-trained AI models in medical devices.
Read the paper: Evaluating Pre-trained 3rd Party AI Models in Medical Device Software Development for Responsible and Ethical Use (AICS 2025). Our evaluation SOP, work instruction and checklist are available in the .
Faster Development, Without Cutting Corners
We use AI tools to speed up the work around the code, such as drafting requirements and tests, reviewing code and keeping traceability up to date. They are controlled like any other development tool: assessed for their intended use, with every output reviewed by a qualified engineer.
Assessed Before Use
AI tools are assessed for their intended use with our Oversure framework and documented in the software development plan.
Reviewed by Engineers
Qualified engineers review and approve every AI output before it enters your code or documentation. AI drafts; people decide.
Traceable & Controlled
AI-assisted work goes through the same code review, testing and change control as any other change to your software.
Find out how we validate AI tools:
Sustainable by Design
Software has an environmental footprint too: the energy used by servers, cloud services and AI models, the data it stores and moves, and the hardware it runs on and eventually retires. We build ecodesign into the same lifecycle, guided by IEC 62430 and our work on IEC 63686, without compromising safety or performance.
Environmental Requirements
Objectives such as energy use, data volumes and supported hardware are captured as design inputs, alongside safety and performance.
Efficient Compute & AI
Right-sized cloud infrastructure, efficient models and inference, and data retention that keeps only what is needed.
Longer Hardware Life
Supporting existing devices and platforms for longer, with lean updates instead of forced hardware replacement.
Responsible End of Life
Planned retirement with secure data deletion or migration, so nothing is left running or stored without a purpose.
Software and the Evidence Behind It
You get working software and technical documentation that a Notified Body or the FDA can follow from requirement to test result.
Plans
Software development plan, AI development plan, verification plans and the software maintenance plan.
Specifications & Design
Software requirements, architecture and detailed design, with a traceability matrix linking them to tests and risks.
Verification Evidence
Unit, integration and system test records, security test reports and AI performance reports.
Risk & Security Files
Software inputs to your ISO 14971 risk file, threat models, SOUP list and software bill of materials.
Release Package
Release record, known anomalies list, archived build configuration and labelling inputs.
AI Documentation
Data governance records, training records, model card and the AI sections of your MDR and AI Act technical documentation.
Building Medical Device Software?
Tell us about your device, your intended use and where you are today, and we will propose a development plan that fits your regulatory pathway.
AI Automation Services
for MedTech & Life Sciences
QMS · Regulatory · Risk · Operations
We design and build AI automation for regulated organisations: tools that draft, check, triage and analyse so your teams spend their time on judgement. Every solution is built with human oversight and validated before it goes live, using our AI Validation framework.
Three Areas Where AI Saves Real Time
We combine 30 years of life sciences experience, across pharma and medical devices, with hands-on software and AI engineering, so automation fits the way regulated teams actually work.
QMS & Regulatory Workflows
Document drafting and review, change assessments, CAPA and complaint triage, audit preparation, and regulatory intelligence, built around your procedures and records.
Risk & Safety Analysis Support
AI-assisted hazard identification, risk management file checks and post-market data review, with human-in-the-loop approval at every decision point.
Business Process Automation
Workflow automation, reporting and system integrations that remove repetitive manual work from operations and support functions.
Built for Audit from Day One
In regulated work, an automation is only useful if you can show it is fit for purpose. We validate AI-enabled processes with Oversure, our AI assurance framework, so the evidence is ready when an auditor asks.
From First Conversation to Live Operation
Discover
We map the process, the data and the risks, and agree where automation will pay off.
Pilot
A small working automation on real documents or data, with your team reviewing the output.
Validate
Intended use, acceptance criteria, testing and ongoing monitoring documented for your quality system.
Operate
Go-live with change control, performance monitoring and updates as models and processes evolve.
AI-Enabled Tools for Life Sciences
We use the same approach in our own products: AskRiskie 2.0 for AI-assisted risk management and AIaCMP for AI-enabled change assessment, both with human review at key decision points.
Which Process Would You Automate First?
Tell us where your teams lose the most time and what regulations apply, and we will suggest a starting point and a plan to validate it.
Change Management for AI
in Regulated Organisations
GMP · ISO 13485 · EU MDR & IVDR · EU AI Act · FDA PCCP
Introducing AI is a change, and in a regulated organisation every change has to be identified, assessed, controlled and shown to work. We guide AI projects from first idea to live operation: identifying where AI adds value, planning and designing the change, developing and testing it, implementing it with your teams, and assessing whether it delivered what you intended.
A Gated Model for AI Change
Our model brings together two foundations of change and quality: Lewin's unfreeze, change and refreeze, and Deming's Plan–Do–Check–Act cycle, with the stage gates regulated organisations already use for design control. Technology and people move forward together, nothing moves on until it has been signed off, and what we learn feeds the next change.
Prepare
Build the case, the coalition and the plan.
- 1IdentifyWhere AI helps, and where it shouldn't be used
- 2PlanIntended use, scope and regulatory route
Change
Design, build and prove the solution.
- 3DesignThe solution and how people will work with it
- 4DevelopBuild or configure under a controlled lifecycle
- 5TestVerify, validate and test usability
Sustain
Embed the change and prove it worked.
- 6ImplementStaged roll-out, training and updated procedures
- 7AssessEffectiveness, performance and reliance on the AI
Four Gates, Four Sign-offs
Each gate is a documented decision in your quality management system, with named approvers, so every step's outputs are captured before the change moves on.
Change Approved
Prioritised use cases and intended use, change classification and regulatory route (process change, GMP change control, significant change or PCCP), change plan and stakeholder map.
Design Approved
Requirements, risk analysis, human oversight and user interface design, data flows, cybersecurity and supplier controls for any third-party AI.
Release Approved
Verified build and traceability, validation (in line with GAMP 5 where it applies) and usability evidence, training ready, and any regulatory submission or notification completed.
Change Closed
Effectiveness review against the intended outcomes, adoption confirmed, monitoring plan in place and change records complete.
The model draws on Kurt Lewin's three-stage model of change, the Plan–Do–Check–Act cycle popularised by W. Edwards Deming, and the stage gates of design control. It is also informed by wider change management practice, including John Kotter's work on leading change and Prosci's ADKAR® Model, but it is our own approach and does not reproduce them. ADKAR® is a registered trademark of Prosci, Inc.
Across Your Quality System, Operations and Products
AI in Your Quality & Regulatory Work
Adopting AI in quality, regulatory, clinical or business processes, from document drafting to complaint triage and regulatory intelligence. We manage the change under your quality system, validate the AI with our Oversure framework, and address the EU AI Act where it applies.
AI in GMP Operations
Introducing AI into pharma and biotech manufacturing, laboratories and quality control. We take the change through GMP change control, with risk-based validation in line with GAMP 5 and computer software assurance, and data integrity built in.
AI in Medical Devices & IVDs
Retraining a model, adding data sources or changing performance in an AI-enabled medical device or IVD. We help you decide whether the change is significant, prepare a PCCP where appropriate, and keep your technical documentation and users up to date.
AI Projects Succeed or Fail on Adoption
The technology is rarely the hardest part. We help leaders, quality teams and users understand the change, so AI is used as intended and trust in it stays at the right level.
Leadership & Governance
Clear ownership, decision rights and an AI policy that fits your quality system.
Stakeholders & Communication
Involve the people affected early, from frontline users to your notified body.
Competence & Training
Role-based training so people know what the AI can and cannot do.
Human Oversight
Review points and escalation routes that keep people in charge of the decisions that matter.
Where Does Your Change Governance Stand?
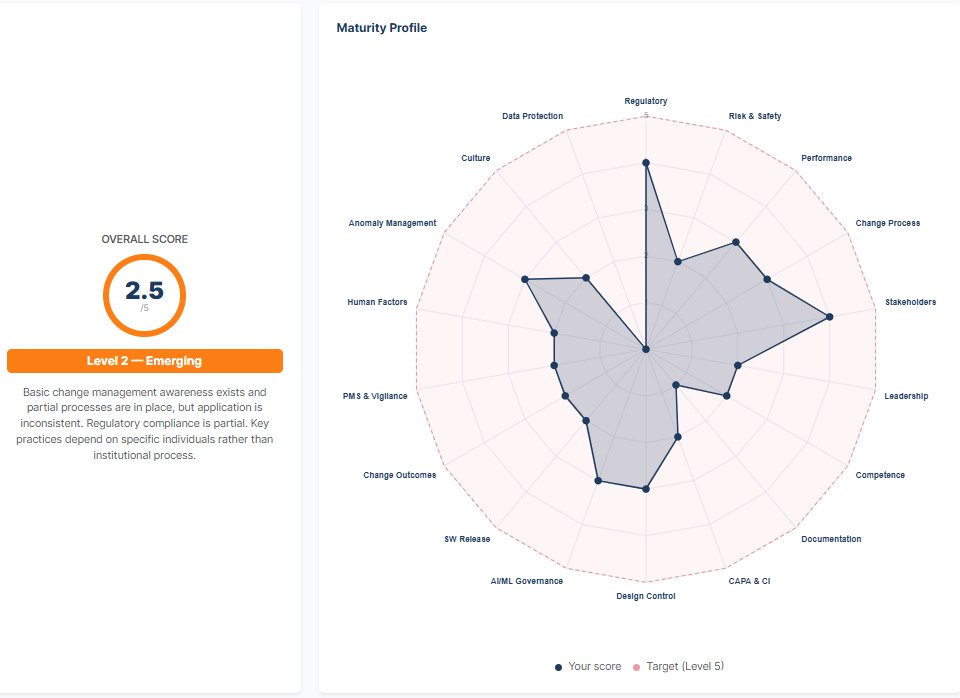
Start with our free Change Governance Maturity Assessment. It benchmarks your organisation across 18 domains, including AI/ML governance, and gives you a maturity score, recommendations for each domain and a PDF report.
Grounded in research. Our approach draws on Niamh St John Lynch's doctoral research into regulatory change management for AI-enabled medical devices, and on her work on international standards for AI in medical devices.
Planning an AI Project?
Tell us what you would like AI to do and where it will be used. We will help you scope the change, choose the regulatory route and plan how to deliver it.
Whitepapers & Frameworks
Practical guidance on regulation, standards and AI for medical devices and life sciences
Our whitepapers turn research and standards work into methods you can use in your own organisation. They are free to download. Peer-reviewed publications are listed on the Research page.
Latest Whitepapers
Data Integrity and AI in GxP
What is required, what is proposed, and what still has to be worked out when AI is used in regulated manufacturing and quality systems, across pharma and biotech, medical devices and IVDs, in the EU, UK and US.
Includes status tables for every relevant instrument, what the EMA's Annex 22 workshop concluded, how to build a control strategy, a cross-sector comparison and the six questions still open.
By Niamh St John Lynch · St John Lynch & Co · PDF, 31 pages
IEC TS 62366-3: Usability Engineering for AI-Enabled Medical Devices
A practical guide to the first Committee Draft of IEC TS 62366-3: what it says, how it fits with IEC 62366-1, ISO 14971, EU MDR, the EU AI Act and FDA expectations, and how to build it into your existing usability engineering process.
Includes a 90-day implementation plan, a fully worked example for a fictional AI sepsis early-warning system, guidance for generative AI and AI agents, and complementary methods such as STPA and situation awareness that find the risks a single-user analysis can miss.
By Niamh St John Lynch · St John Lynch & Co · PDF, 19 pages
Oversure™: A Framework for Validating AI Used in Regulated Processes
An original framework for deciding how much validation an AI use needs, carrying it out, and keeping that use under control for as long as it runs. Written for medtech, medical device, IVD, pharma and biotech organisations.
The full document includes the five-step method, seven principles, three assurance tiers, two fully worked examples, alignment tables against MDR, IVDR, GMP and the EU AI Act, a comparison with FDA's Computer Software Assurance approach, and supporting templates.
By Niamh St John Lynch · St John Lynch & Co · Word document
What Should We Write Next?
Is there a regulatory, standards or AI topic you would like a practical whitepaper on? Tell us, and it will help us decide what to publish next.
IEC TS 62366-3
Usability Engineering for AI-Enabled Medical Devices
A practical guide to the first Committee Draft · Version 2.0 · October 2026
IEC TS 62366-3 explains how to apply IEC 62366-1 to medical devices that use AI. Our white paper sets out what the draft says, how it fits with ISO 14971 and regulation, and how to build it into your existing usability process, with a fully worked example you can follow.
AI Moves Use Error from the Hands to the Head
The draft adds no new mandatory requirements. It shows how each step of the IEC 62366-1 process adapts when the biggest dangers are cognitive: misreading a probability, trusting the AI too much or too little, or not knowing where it is weak. For manufacturers, that means five things.
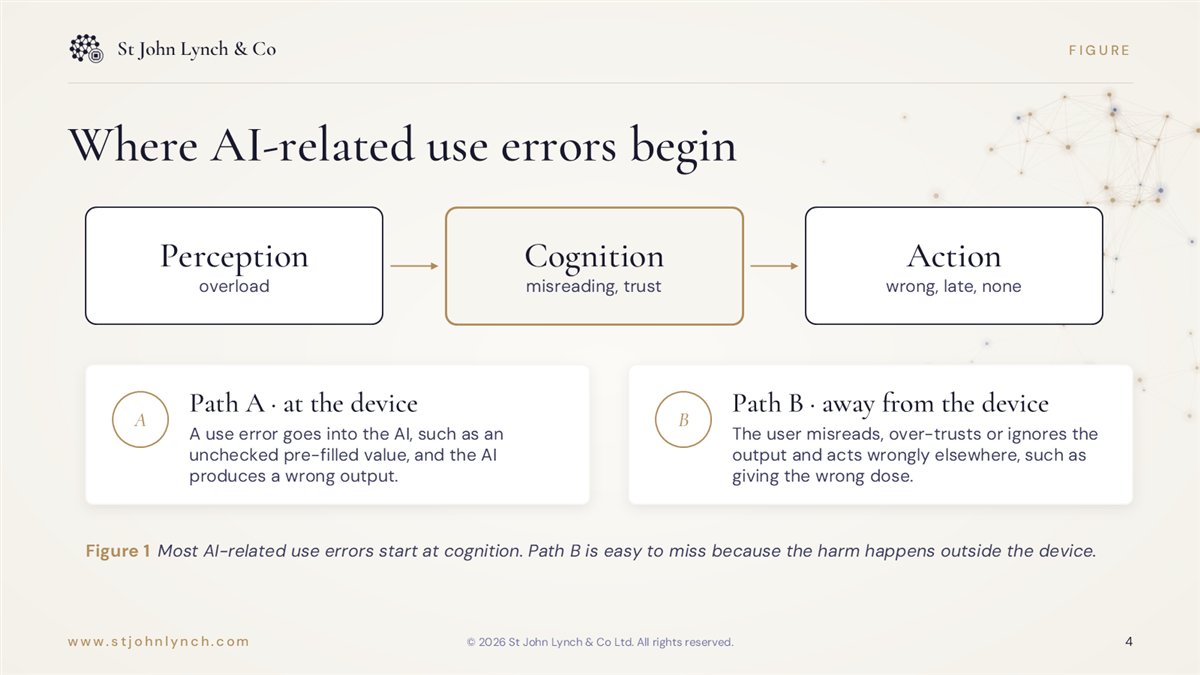
Where AI-Related Use Errors Begin
Most AI-related use errors start at cognition, where outputs are interpreted and trusted. The resulting action either feeds bad input into the AI (Path A) or causes harm elsewhere (Path B). Path B is easy to miss because the harm happens outside the device being assessed.
Built to Be Used, Not Just Read
From Draft to Procedure
A clause-by-clause map from IEC 62366-1 to what Part 3 adds for AI and the evidence to produce, with a 90-day plan and links to ISO 14971, IEC 62304, EU MDR, the EU AI Act and FDA.
An AI Sepsis Early-Warning System
A fictional device taken through seven steps: use specification, contributing factors, Path A and Path B hazards, a use scenario, testable UI requirements, evaluation and post-market plan.
Generative AI, Agents & Beyond PCA
Use errors and design patterns for generative AI and AI agents, and how STPA and situation awareness find risks that a single-user analysis can miss.
The Summary in Eight Slides
The key points, figure and worked example as a short slide deck. Free to view and easy to share with your team.
Get the Full White Paper
All 19 pages, including the worked example, the complementary methods and the full references.
Data Integrity
and AI in GxP
What is required, what is proposed, and what still has to be worked out · Version 1.0 · November 2026
How the data integrity rules apply when AI is used in regulated manufacturing and quality systems, across pharma and biotech, medical devices and IVDs, in the EU, UK and US. Our white paper keeps what is in force, what is proposed and what is still open clearly apart.
The Type of Model Is Not the Deciding Factor
Across every sector, regulators are reaching the same position: whether an AI application is acceptable depends on its intended use, the risks it presents and how well those risks are controlled over its lifecycle. For quality teams, that means five things.
No Single Control Catches Every Failure
The EMA's Annex 22 workshop described three layers of control around a model. Each layer addresses particular failure modes, and the regulated record at the end still has a named person accountable for it.
- Context-of-use checks
- Out-of-distribution checks
- Rule-based input limits
- Retrieval with source binding
- Uncertainty measures
- Consistency across runs
- Confidence gates
- Human review gate
- Fallback to a validated state
Clear on What Applies Today
Where Each Instrument Stands
Every relevant instrument for pharma, devices and IVDs across the EU, UK, US and PIC/S, with its date and whether it is in force, a draft or industry guidance.
From the Workshop to Practice
Layered controls, human oversight versus human-in-the-loop, the AI qualification package, and the supplier and cloud evidence you will need.
Pharma, Devices and IVDs Compared
Applying CSA to AI, making expert review auditable, the two dimensions of risk, and a side-by-side comparison of how each sector is assessed.
The Summary in Eight Slides
The key points, figure and open questions as a short slide deck. Free to view and easy to share with your team.
Get the Full White Paper
All 31 pages, including the status tables, the cross-sector comparison and 47 references.
Regulatory Strategy
for Global Market Access
EU · UK · US · Canada · Australia · Japan · Brazil
Choosing the right markets, in the right order, with evidence you can reuse. We help medical device, software and AI-enabled device manufacturers plan classification, regulatory pathway and evidence strategy across territories, so one well-built technical file and quality system open several doors.
One Plan, Several Markets
Most manufacturers do not need to start again for every territory. We build a strategy around what your device is, who will use it and where you want to sell, then plan the work so each market adds as little new effort as possible.
Qualify & Classify
Is it a medical device, and in which class in each market? We settle this early, especially for software and AI.
Choose Pathways
The route to each market, the conformity or clearance route it needs and the order that makes commercial sense.
Reuse Evidence
A quality system and technical file built on common ground, such as ISO 13485, that adapts to each regulator.
Stay Compliant
Post-market surveillance, changes and renewals planned for every territory you enter.
EU MDR, IVDR & the AI Act
The EU framework is the most demanding for many manufacturers, and it underpins other strategies. We guide you from qualification and classification through Notified Body engagement, technical documentation, clinical evidence and the interaction with the EU AI Act for AI-enabled devices.
UK MDR & the MHRA
Great Britain has its own regime, and Northern Ireland has separate arrangements. The right strategy depends on where you place the device and which marks you already hold.
UKCA & CE Recognition
Planning your route to market in Great Britain, including how long CE marking is accepted and when UKCA marking becomes necessary for your device.
MHRA Registration & UK Responsible Person
Device registration with the MHRA and the UK Responsible Person role for manufacturers based outside the UK.
Software and AI as a Medical Device
Classification, evidence and change management for software and AI-enabled devices, in line with the MHRA's evolving approach.
FDA Pathways & QMSR
The FDA regulates by risk class and by pathway. We help you decide between 510(k), De Novo and PMA, plan the evidence that FDA expects and align your quality system with the Quality Management System Regulation.
Classification & Pathway
Device classification, predicate strategy and the choice between 510(k), De Novo and PMA, including when to talk to FDA early.
QMSR & Establishment Requirements
Aligning your ISO 13485 system with the QMSR (21 CFR Part 820), plus establishment registration, device listing and the US agent for non-US manufacturers.
Digital Health Expectations
Software documentation, predetermined change control plans for AI-enabled device software and premarket cybersecurity expectations.
Canada, Australia, Japan & Brazil
Beyond the EU, UK and US, we plan entry into further markets. Several of them participate in the Medical Device Single Audit Program (MDSAP), so one audit of your quality system can support more than one market.
Health Canada
Device licensing, classification and the role of MDSAP certification in your application.
TGA
Inclusion on the Australian Register of Therapeutic Goods and the local sponsor requirement.
PMDA & MHLW
Marketing authorisation holder arrangements, classification and the route to approval or certification.
ANVISA
Registration pathways and the local registration holder, with MDSAP as part of the plan.
Other markets can be added on request. Regulatory requirements change, and we confirm the current position for each territory at the start of every engagement.
Which Markets Are on Your Roadmap?
Tell us about your device and where you want to sell it, and we will outline a regulatory strategy with the pathway, evidence and timeline for each market.
Privacy Notice
Last updated: 21 October 2026
Who we are
St John Lynch & Co Ltd (company no. 738996), Derrycallan North, Gort, Co. Galway, Ireland, is responsible for the personal data collected through this website. You can contact us at info@stjohnlynch.com.
What we collect and why
- Contact form and email. Your name, email address, the subject and your message, so we can reply to your enquiry. Our legal basis is our legitimate interest in answering enquiries and, where you ask about our services, steps taken at your request before a contract.
- Free downloads. Your name, email address and organisation, and your role if you give it, so we can provide the resource you asked for and understand who is using it. Our legal basis is our legitimate interest in sharing our work. We send you emails about new resources only if you tick the box to ask for them (your consent), and you can unsubscribe at any time.
- Training and programme requests, and whitepaper topic suggestions. The details you enter, used to respond to your request or plan our work. An email address on a topic suggestion is used only to tell you when a whitepaper on that topic is published.
- Careers. Any CV and details you email us, used only to consider your application.
- Booking a consult. Bookings are made on Microsoft Bookings, which collects the details you enter there.
- Purchases. Toolkit packs are sold through Payhip. Payhip processes your payment and details; we do not see your card information.
Cookies and similar technologies
We do not use analytics, advertising or tracking cookies. Your browser stores your language choice (so the site opens in English or French as you prefer) and whether you have closed the announcement bar. These stay on your device and are not sent to us. Our fonts are loaded from Google Fonts, so your IP address is sent to Google when a page loads.
Who we share data with
We use a small number of service providers to run the site: Formspree (form handling), Microsoft (bookings), Payhip (payments) and our website and email hosting provider. They process data on our behalf or, for Microsoft Bookings and Payhip, under their own terms. We do not sell your data. Some of these providers are based outside the European Economic Area. Where that is the case, transfers rely on safeguards such as the EU–US Data Privacy Framework or Standard Contractual Clauses.
Links to other sites
This site links to other websites and tools, such as LinkedIn, ORCID, DkIT STÓR, OpenStreetMap and the Change Governance Maturity Assessment. They have their own privacy practices, and we are not responsible for them.
How long we keep data
We keep enquiries, download requests and application emails only as long as we need them to deal with the matter and for reasonable record-keeping, then delete them.
Your rights
You can ask us to give you a copy of your personal data, correct it, delete it, restrict or stop our use of it, or transfer it to you. Where we rely on your consent, you can withdraw it at any time. Email info@stjohnlynch.com and we will respond within one month. You also have the right to complain to the Data Protection Commission in Ireland (dataprotection.ie) or to your local data protection authority.
The e-learning course
Our free e-learning courses have their own privacy notice.
Changes to this notice
We will update this page if our practices change, and show the date of the latest update at the top.
Oversure™
A Framework for Validating AI Used in Regulated Processes
Oversure is an original framework for deciding how much validation an AI use needs, carrying it out, and keeping that use under control for as long as it runs. Written for medtech, medical device, IVD, pharma and biotech organisations, it answers one question: how do you show that a specific use of AI in a regulated process is fit for purpose, that the people overseeing it can catch it when it is wrong, and that it stays that way?
Validating AI Used in Your Quality & Regulatory Workflows
If your teams use AI to draft documents, review records, classify complaints or analyse data, auditors and regulators will expect evidence that it is fit for its intended use. We carry out that validation with you, using the Oversure framework, so the evidence is proportionate, recorded and ready for audit.
Quality Management Workflows
Document drafting and review, CAPA and nonconformity handling, complaint triage, internal audit preparation and training records.
Regulatory Workflows
Technical documentation drafting, regulatory intelligence, literature screening for clinical evaluation and submission support.
Surveillance & Vigilance
AI that analyses complaints, trends and post-market data, or helps classify incidents for reporting.
Manufacturing, Lab & Supplier
AI used in process control, laboratory operations, supplier management or knowledge work that feeds a regulated record.
What We Deliver
Scope & Classify
An inventory of your AI uses, and a classification of each by consequence, oversight and reliance, so effort goes where the risk is.
Plan, Test & Document
Validation plans, intended-use definitions, acceptance criteria, test protocols and reports that fit your quality system.
Oversight & Control
Human-oversight design, procedures, staff training, performance monitoring and change control for as long as the AI is used.
One Question, Answered Systematically
Validating AI in a regulated process is not only software testing. It is a proportionate, recorded demonstration that a specific use of AI is fit for purpose, that the people overseeing it can catch it when it is wrong, and that it stays that way for as long as it is used.
Oversure applies to AI used inside regulated processes — quality management, manufacturing and process control, laboratory operations, regulatory affairs, post-market surveillance and vigilance, clinical operations support, and supplier, training or knowledge management work that feeds a regulated record. It applies equally to general business AI tools, such as chat assistants, when they are used for any of those tasks.
It does not apply to AI that forms part of, or is itself, a medical device or IVD. Every AI use passes an exit gate in Step 1: if the AI is part of a device, or its output informs the diagnosis, treatment or monitoring of an individual patient, the use leaves this framework and is referred to the product regulatory route.
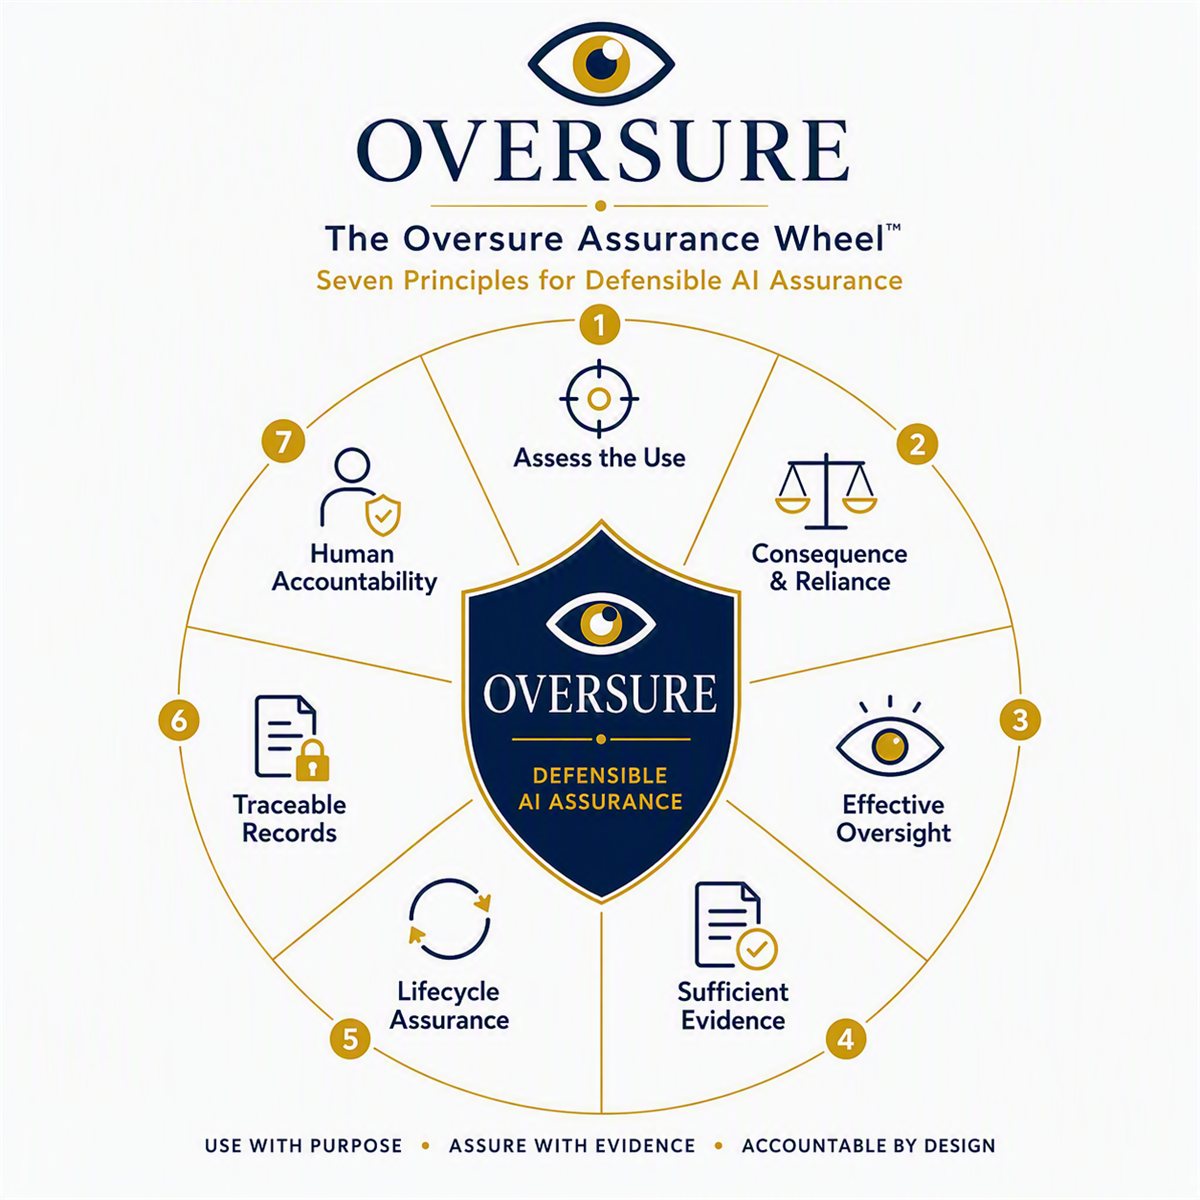
Seven Principles
Every requirement in Oversure traces back to at least one of these principles.
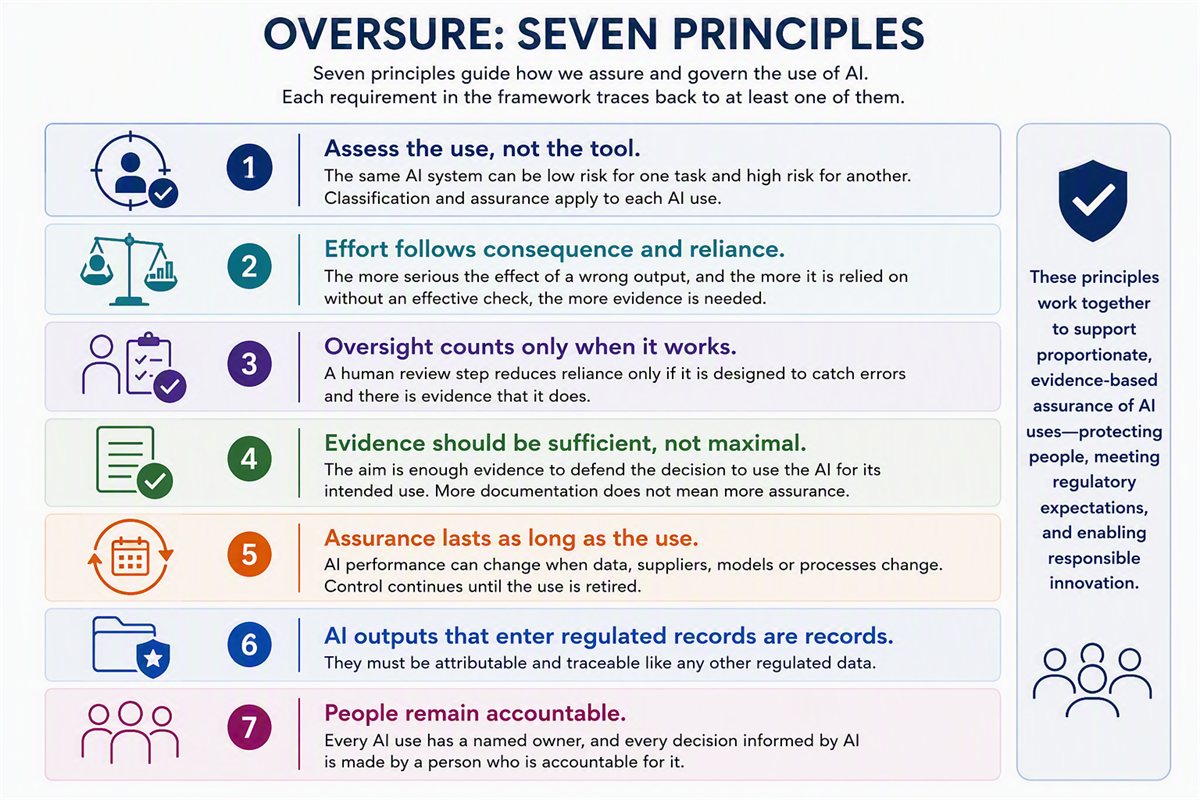
The same AI system can be low risk for one task and high risk for another. Classification and assurance apply to each AI use, not to the tool as a whole.
The more serious the effect of a wrong output, and the more it is relied on without an effective check, the more evidence is needed.
A human review step reduces reliance only if it is designed to catch errors and there is evidence that it does.
The aim is enough evidence to defend the decision to use the AI for its intended use. More documentation does not mean more assurance.
AI performance can change when data, suppliers, models or processes change. Control continues until the use is retired.
Evidence generated in support of an AI use must be attributable and traceable, like any other regulated data.
Every AI use has a named owner, and every decision informed by AI is made by a person who is accountable for it.
Five Steps, Every Time
Every AI use goes through the same five steps. Only the depth of work changes with the tier — for a Tier 1 use, Steps 1 to 3 can be completed as a single short assessment.
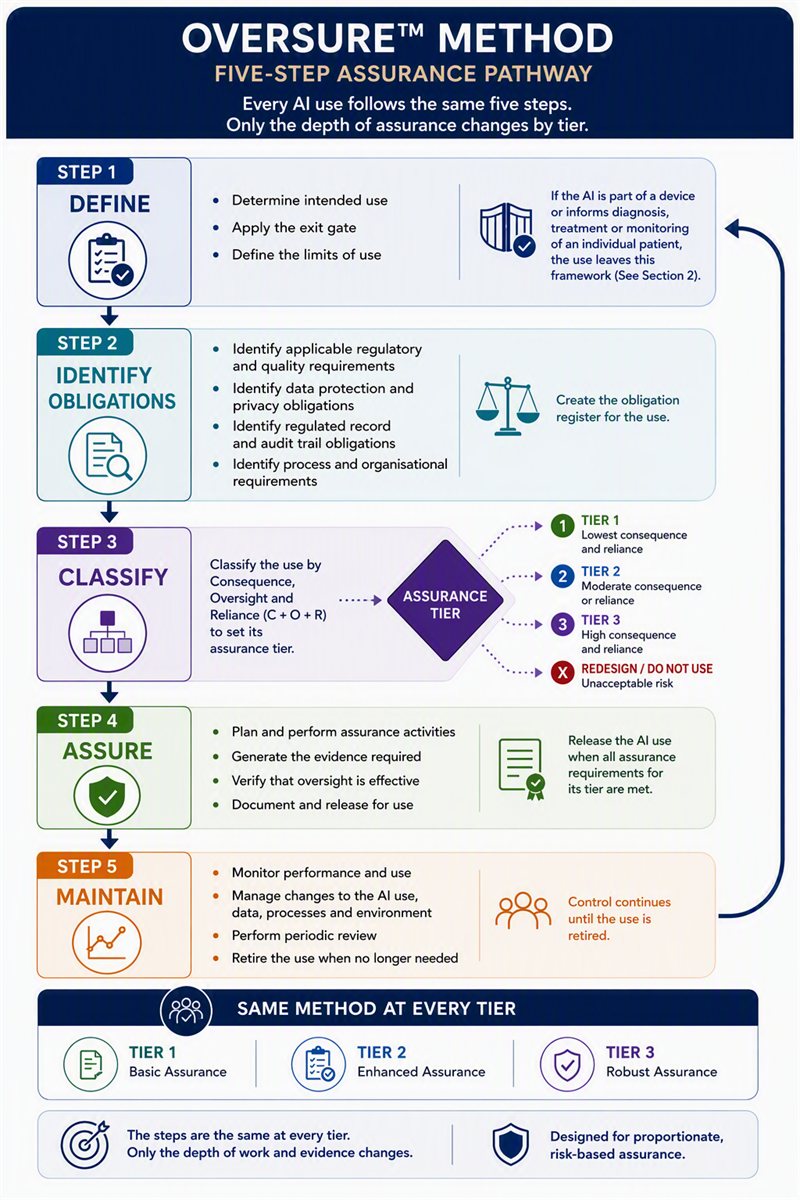
Consequence, Oversight & Reliance Set the Tier
Classification is not a checklist — it is an equation. Consequence is rated first, oversight second, and the strength of that oversight determines how much reliance on the output can be justified. Consequence and reliance together set the assurance tier.
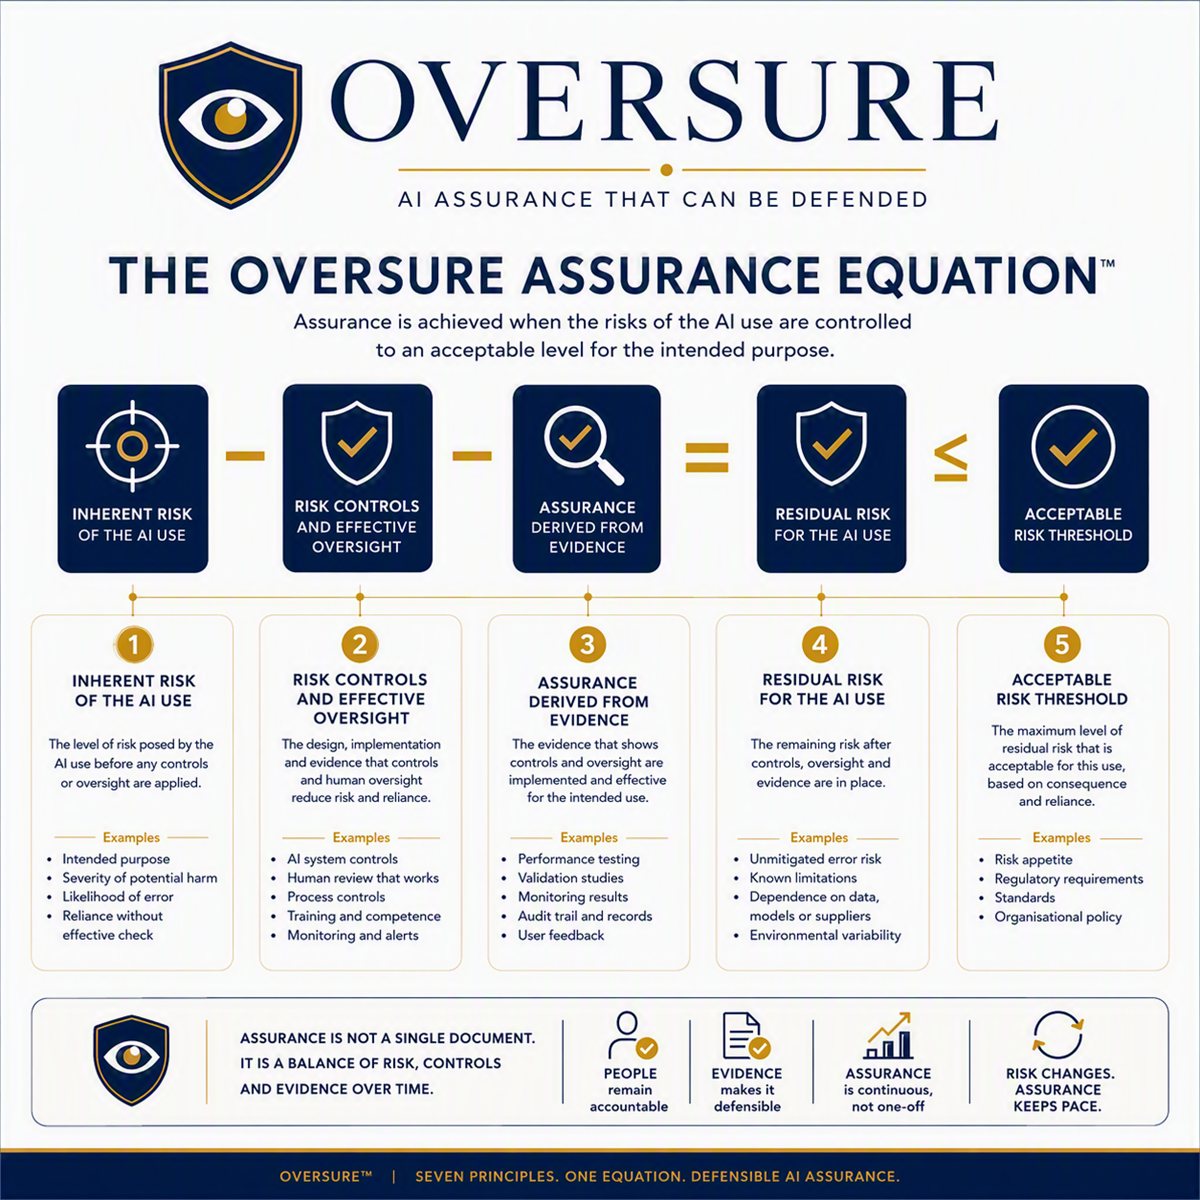
What happens if it's wrong?
C1 — no direct effect on quality, safety or record integrity.
C2 — feeds a regulated record subject to later independent review.
C3 — feeds a release, safety, risk or submission decision.
Is the review real?
O0/O1 — no review, or a nominal check that receives no credit.
O2 — informed review: competent, resourced, recorded.
O3 — verification by design, built into the workflow itself.
How much is it trusted?
R1 — fully, independently checked before use.
R2 — reviewed, but the reviewer depends on it substantially.
R3 — used as it comes, or not realistically checkable.
| Consequence | R1 | R2 | R3 |
|---|---|---|---|
| C1 — Low | Tier 1 | Tier 1 | Tier 2 |
| C2 — Medium–Significant | Tier 1 | Tier 2 | Tier 3 |
| C3 — Critical | Tier 2 | Tier 3 | Redesign |
A use rated C3 and R3 does not proceed. The answer to high consequence and high reliance is to redesign the workflow so reliance falls — usually by building verification by design — not to test the AI harder.
The Same Task, Deployed Four Ways
How an AI is deployed changes who controls the model and the workflow — and that changes what's needed. Take one task: drafting a first-draft deviation description from investigator notes, for QA review. Consequence is C2 in every case.
| Deployment | Outcome |
|---|---|
| D1 — Personal public tool | Not permitted. Confidential data on an uncontrolled tool. |
| D2 — Enterprise assistant | Permitted with QA review against the notes. Tier 2 |
| D3 — Feature in the eQMS | Permitted once classified; vendor evidence leveraged. Tier 2 |
| D4 — In-house tool | Each sentence traced to its source, QA confirms by design. Tier 1 |
Good workflow design can lower the tier more than additional testing ever can. Oversure defines seven deployment types in total — from personal public tools (D1) through to agentic AI taking actions in other systems (D7) — each with its own typical modifiers and framework position.
Built to Sit Alongside What You Already Do
Oversure is an original framework — it does not depend on any single external source — but it is deliberately designed to align with the regulations, standards and guidance already in use across medtech, pharma and biotech.
Annex B of the framework sets out its relationship to FDA's Computer Software Assurance guidance in detail. Auditors already familiar with CSA will recognise the reasoning: Oversure follows the same risk-based, evidence-proportionate logic, then extends it to deal with how AI actually fails — non-determinism, fabrication, drift, and model changes a supplier makes without notice.
A Worked Example
Adverse event retrieval for a risk file — a tool retrieves candidate reports from the FDA MAUDE database so a risk management team can consider real-world failure data.
The output feeds risk acceptability decisions, so consequence is C3. In the first design, users were simply asked to "check the results" — nominal oversight (O1) — giving reliance R3 and the redesign outcome. The workflow was redesigned: the tool now presents the exact search used alongside a sample of results, so the user can reproduce the search at source and confirm it before results can be added to the risk file. That's verification by design (O3). Reliance falls to R1, and the use becomes Tier 2 — with repeatability testing added because retrieval is non-deterministic.
This is one of two full worked examples in the framework document, each carried through all five steps with the reasoning shown at every decision point.
Seven Principles, One Framework
Applying the seven principles with the methods for assurance assessment gives a single, defensible wheel of AI assurance for regulated life science processes.
Get the Full Framework
The complete Oversure document includes the full method, all seven deployment types, statistical monitoring guidance, role definitions, two fully worked examples, alignment tables against MDR, IVDR, GMP and the AI Act, a detailed comparison to FDA's Computer Software Assurance approach, and a full set of supporting templates. It's free to download. Training on the framework is available from St John Lynch & Co on request, and I'm available to help organisations put it into practice.
Oversure is a trademark of St John Lynch & Co Ltd (registration pending). © St John Lynch & Co Ltd. All rights reserved.
Building Regulatory & Technical Capability
Health Software · AI-Enabled Medical Devices · EU MDR/IVDR
UK MDR · QMSR · AI
Act · Standards
Drawing on 30+ years in the life sciences — including experience as a Notified Body technical reviewer and site auditor, IRCA-certified Lead Auditor training in ISO 9001 and ISO 13485, and work with organisations such as Boston Scientific, J&J, Abbott, Medtronic, Novartis, Mylan (now Viatris) and Olympus — I deliver targeted training programmes that equip industry teams with practical, up-to-date knowledge of the regulatory landscape for AI-enabled medical devices.
IEC 62304 Essentials — Free Online Course
A free self-paced course covering all 13 IEC 62304 process areas at two levels — an Introductory level for those new to the standard, and an Advanced level with full clause references for experienced practitioners. Study at your own pace, then test your knowledge with a timed 15-question assessment. Score 80% or higher to download a certificate of completion.
13 Process Areas, Two Levels
Introductory content for those new to IEC 62304 and full clause-referenced Advanced content for experienced practitioners — switch level at any time, filterable by safety class.
Timed Quiz
15 multiple-choice questions with immediate feedback. Separate Introductory and Advanced question sets align with the level you studied at. 60 seconds per question.
Downloadable Certificate
Score 80% or higher and download a certificate of completion — useful for CPD records and team training evidence.
IEC 62304 Edition 2
The next edition of IEC 62304 is under active development at IEC TC62. Key proposed changes include:
- Expanded scope to cover health software broadly, aligning with IEC 82304-1
- Two Software Process Rigor Levels replacing the three safety classes (A, B, C)
- Softened normative references to ISO 13485 and ISO 14971
- Legacy software provisions moving to an informative annex
Training updated for Edition 2 will be published here as the standard is finalised. This course reflects the current published standard: IEC 62304:2006+AMD1:2015.
Training Programmes for Industry
Each programme is designed for regulatory affairs, quality, and engineering professionals working on medical devices — combining regulatory theory with practical application and the latest developments from standards committees and doctoral research.
Navigating the AI Act for Medical Device Manufacturers
A practical introduction to EU AI Act obligations for manufacturers of AI-enabled medical devices — covering high-risk AI system classification, Article 22 requirements, conformity assessment routes, and interaction with EU MDR 2017/745.
AI/ML Software Lifecycle for Medical Devices
Practical training on IEC 62304 software lifecycle requirements as applied to AI/ML-enabled devices — addressing adaptive algorithm change management, post-market surveillance obligations, and risk management under ISO 14971.
AI Governance Frameworks in Practice
Workshop-based training on implementing AI governance in a medical device organisation — using ISO 42001 and BS 30440:2023 as practical frameworks alongside the ChangeIQ methodology developed through doctoral research.
MDR Compliance for AI-Enabled Devices
In-depth training on EU MDR 2017/745 obligations specific to software and AI-enabled medical devices — including technical documentation requirements, PMCF obligations, and the implications of the EC Simplification Digital Package.
Emerging Standards Briefing
A regularly updated briefing programme on the current and emerging standards landscape for AI-enabled medical devices — drawing directly on active participation in IEC TC62, NSAI/ETC/TC10, and CEN-CENELEC AI Task Groups 1 & 2.
Custom In-House Training
Tailored training designed around your organisation's specific regulatory context, product portfolio, and team needs. Suitable for regulatory, quality, and R&D teams at any stage of MDR or AI Act readiness.
Medical Device & IVD Software — Modular Training Programme
A menu of focused sessions on the regulation, standards, and quality management of Software as a Medical Device (SaMD), Software in a Medical Device (SiMD), Clinical Decision Support Systems (CDSS), and in-vitro diagnostic (IVD) software. Each session runs two hours and can be delivered online or on-site. Sessions are modular — select the topics most relevant to where your organisation is in development, in any combination. Session 1 is the recommended foundation and is included as a minimum, as it provides the regulatory and standards grounding the other sessions build on; the remaining sessions can be chosen freely.
| # | Training Session | Key Standards & Frameworks | Select |
|---|---|---|---|
| 1 | Regulations & Standards Overview for Medical Device & IVD Software
Recommended Foundation
The regulatory landscape and core standards for software that is, or is part of, a medical device or IVD — the essential grounding for every other session. |
EU MDR 2017/745 · EU IVDR 2017/746 · FDA SaMD · IEC 62304 · ISO 14971 · ISO 13485 | |
| 2 | What is SaMD? Qualification & Classification
Determining whether software qualifies as a medical device and how it is classified across the EU and FDA frameworks. |
IMDRF SaMD framework · MDCG 2019-11 · MDR Rule 11 · FDA SaMD categories | |
| 3 | IVD Software — Qualification, Classification & Specifics
How software is qualified and classified under the IVDR, including software that drives or influences an IVD, companion diagnostics and accompanying software. |
EU IVDR 2017/746 · MDCG 2019-11 · IVDR classification rules | |
| 4 | Clinical Decision Support Systems (CDSS)
When clinical decision support qualifies as a medical device and when it does not — the criteria that distinguish device CDS from exempt decision support, and the obligations that follow under the EU and FDA frameworks. |
FDA CDS guidance (2022) · MDR Rule 11 · MDCG 2019-11 · IMDRF SaMD | |
| 5 | Software Development Lifecycle — IEC 62304
The software lifecycle processes and software safety classification (Class A/B/C), and how they shape your development plan. |
IEC 62304 · IEC 82304-1 | |
| 6 | Software in a Medical Device (SiMD) & Medical Electrical Equipment
Where software is embedded in medical electrical equipment (SiMD rather than SaMD): how IEC 62304 interfaces with the IEC 60601 series, including programmable electrical medical systems (PEMS) and the related risk and usability collateral standards. |
IEC 60601-1 (Clause 14, PEMS) · IEC 60601-1-x collaterals · IEC 62304 | |
| 7 | Software Risk Management
Applying ISO 14971 to software — identifying how software can contribute to hazardous situations and designing effective risk controls. |
ISO 14971 · ISO/TR 24971 · IEC 62304 (risk) | |
| 8 | Software Requirements & Architecture
Eliciting and managing software requirements and defining architecture and detailed design with traceability through the lifecycle. |
IEC 62304 · requirements & architecture practice | |
| 9 | Verification & Validation of Software
Building a V&V strategy — unit, integration and system testing, test management and traceability to requirements and risk. |
IEC 62304 · FDA software validation / CSA | |
| 10 | SOUP, Off-the-Shelf & Open-Source Software
Managing software of unknown provenance, third-party and open-source components, including the software bill of materials (SBOM). |
IEC 62304 (SOUP) · SBOM · FDA OTS guidance | |
| 11 | Software Configuration & Change Management
Version control, configuration items, change control and problem resolution across the software lifecycle. |
IEC 62304 §§6-9 · ISO 13485 | |
| 12 | Cybersecurity for Medical Device & IVD Software
Pre- and post-market security across the lifecycle — threat modelling, secure development and vulnerability management. |
IEC 81001-5-1 · MDCG 2019-16 · FDA premarket cybersecurity | |
| 13 | Usability & Human Factors Engineering
Usability engineering and use-related risk for software interfaces, including formative and summative evaluation. |
IEC 62366-1 · IEC 62366-2 · FDA HFE guidance | |
| 14 | Health Software & Health IT
Standalone health software, mobile and cloud/SaaS delivery, and product-level safety considerations beyond the device itself. |
IEC 82304-1 · IEC 80001-1 (health IT networks) | |
| 15 | Interoperability & Data Exchange
Connecting software safely — clinical and laboratory data exchange, and the standards that underpin interoperability. |
HL7 FHIR · DICOM · IEC 80001-1 · LIS/LIMS connectivity | |
| 16 | Clinical Evaluation & Performance Evaluation for Software
Generating the clinical and performance evidence expected for software, and how the requirements differ between the MDR and IVDR. |
MDR clinical evaluation · IVDR performance evaluation · MDCG guidance | |
| 17 | IVD Performance Evaluation
Scientific validity, analytical performance and clinical performance for IVD software, and structuring the performance evaluation plan and report. |
IVDR Annex XIII · ISO 15189 context · CLSI guidance | |
| 18 | Quality Management System for Software Teams
Applying ISO 13485 and design controls to software development, including how agile fits within a compliant QMS. |
ISO 13485 · FDA design controls (QMSR) · AAMI TIR45 (agile) | |
| 19 | Technical Documentation & Conformity Assessment
Compiling MDR/IVDR technical documentation for software and what to expect from Notified Body review. |
MDR Annex II/III · IVDR Annex II/III · Notified Body review | |
| 20 | Post-Market Surveillance, Maintenance & Vigilance for Software
Post-market obligations for software — surveillance, maintenance, updates and patches, and incident reporting. |
MDR/IVDR PMS · PMCF/PMPF · software maintenance & vigilance |
AI-specific modules — AI governance, AI Act compliance, and AI risk management — are available separately as part of the AI in Medical Devices programme below. Download the full programme as a PDF.
AI in Medical Devices — Modular Training Programme
A menu of focused sessions on the regulation, standards, and quality management of AI-enabled medical devices — complementing the Medical Device & IVD Software programme above for organisations that need both software-lifecycle and AI-specific training. Each session runs two hours and can be delivered online or on-site. Sessions are modular — select the topics most relevant to where your organisation is in development, in any combination. Session 1 is the recommended foundation and is included as a minimum, as it provides the regulatory and standards grounding the other sessions build on; the remaining sessions can be chosen freely.
| # | Training Session | Key Standards & Frameworks | Select |
|---|---|---|---|
| 1 | Regulations & Standards Overview and Trustworthy AI in Healthcare
Recommended Foundation
The full regulatory landscape for AI-enabled medical devices and the principles of trustworthy AI — the essential grounding for every other session. |
EU MDR 2017/745 · EU AI Act (Reg. 2024/1689) · FDA SaMD · IEC 62304 · ISO 14971 · ISO 13485 · ISO/IEC 42001 | |
| 2 | Introduction to AI — Overview of AI Model Types
Core AI/ML concepts for regulatory, quality and engineering teams, with emphasis on the model types most relevant to medical devices — for example convolutional and vision models for imaging applications, and pre-trained/foundation models. |
Foundational — no single standard | |
| 3 | AI Management System (e.g. ISO/IEC 42001)
Establishing an AI management system and integrating it with an existing ISO 13485 quality system rather than running it in parallel. |
ISO/IEC 42001 · ISO 13485 | |
| 4 | Pre-Trained Models and Evaluation
Evaluating externally sourced and pre-trained models for safety, bias and regulatory acceptability — drawn directly from peer-reviewed published research. |
ISO 14971 · EU AI Act · supporting evaluation frameworks | |
| 5 | Deep Dive into an Example AI-Enabled Device
A worked walkthrough of an example AI-enabled device from concept through to evidence — connecting regulatory theory to a concrete development case (illustrated here with an imaging application, optionally using a modelling tool such as Neural Designer). |
Applied — integrates IEC 62304 / ISO 14971 | |
| 6 | AI Risk Management
AI-specific hazard identification and risk control across the device lifecycle, including data, model and performance-drift hazards. |
ISO 14971 · ISO/TR 24971 (AI risk guidance) | |
| 7 | Software Functions for AI — FDA
The FDA approach to AI/ML software functions and Software as a Medical Device, and how it differs from the EU route. |
FDA SaMD guidance · 21 CFR Part 820 / QMSR | |
| 8 | Software Development Lifecycle & Agentic AI
Applying the software lifecycle to AI/ML components, including IEC 62304 Edition 2 developments and considerations for agentic AI. |
IEC 62304 (incl. Ed.2 developments) | |
| 9 | Predetermined Change Control Plans / Monitoring Plans
Designing PCCPs and monitoring plans so adaptive or updatable models can be maintained without re-triggering full conformity assessment. |
FDA PCCP guidance · EU change-management expectations | |
| 10 | EU AI Act 2024/1689 (as amended) + MDCGs
High-risk AI system obligations, the interplay with EU MDR, and emerging MDCG guidance, reflecting the latest amendments and the EC Simplification Digital Package. |
EU AI Act (Reg. 2024/1689) · EU MDR · MDCG guidance | |
| 11 | AI Data Management
Dataset governance, quality, representativeness and bias — including annotation and labelling provenance. |
IEC PAS 63621 · ISO/IEC 42001 | |
| 12 | AI Data Management — PAS, Example Plan & Report
A practical, worked example of a data management plan and the corresponding report, using the structure of the data-management PAS. |
IEC PAS 63621 (worked example) | |
| 13 | AI Test Methods & Metrics
Verification and validation methods and metrics for AI, including cross-validation and the test-method approaches now emerging in standards. |
IEC 63450 (in development) · V&V methods | |
| 14 | AI Security Risks and Mitigations
Cybersecurity for AI-enabled medical devices — threat modelling, SBOM, and mitigation across the lifecycle. |
IEC 81001-5-1 · EU MDR security requirements | |
| 15 | AI in PEMS — IEC 60601-4-1
AI within programmable electrical medical systems and the concept of degree of autonomy, where the device is also electrical medical equipment. |
IEC 60601-4-1 · IEC 60601-1 | |
| 16 | AI Usability & Human Factors
Usability engineering for AI-enabled devices, including how clinicians interpret and act on AI output. |
IEC 62366-1 · IEC 62366-2 · emerging IEC 62366-3 (AI) | |
| 17 | Performance Evaluation
Analytical and clinical performance evaluation for AI — sensitivity, specificity and AUROC, and standalone versus reader-study designs. |
Performance evidence aligned to EU MDR / FDA expectations | |
| 18 | Post-Market AI Requirements, Maintenance & Change Management
Post-market surveillance obligations specific to AI/ML, ongoing maintenance, and managing change in deployed models. |
EU MDR PMS · EU AI Act · post-market ML surveillance |
Sessions can be tailored to your organisation's specific device type and reduced to one hour each, completed over 9–10 sessions, if preferred. Download the full programme as a PDF.
Flexible Delivery Formats
Training is available in a range of formats to suit your organisation's needs, from half-day workshops to multi-session programmes — delivered online or on-site.
Half-Day & Full-Day Workshops
Focused, intensive sessions designed for regulatory and quality teams who need actionable knowledge quickly. Available as standalone workshops or as part of a series.
Multi-Session Training Programmes
Structured programmes delivered over several sessions, building regulatory capability progressively — suitable for onboarding new team members or upskilling an existing team ahead of MDR or AI Act obligations.
Remote & In-Person Delivery
All programmes are available online or in person. On-site delivery can be arranged across Ireland and the EU. Remote delivery is available globally.
Tailored to Your Context
Content and case studies are adapted to your organisation's device portfolio, regulatory status, and team background — ensuring training is directly applicable to your real-world challenges.
Upcoming Public Training Sessions
The following sessions are planned for open enrolment. Places are limited — contact me to register interest or to discuss in-house delivery on a preferred date.
| Training Programme | Planned Date | Format | Duration | Delivery | Status |
|---|---|---|---|---|---|
| Change Management for Life Sciences | TBC 2027 | TBC | TBC | Online / On-site | Planned |
| Risk Management for Life Sciences | TBC 2027 | TBC | TBC | Online / On-site | Planned |
| MDR Compliance for Software & AI-Enabled Devices | TBC 2027 | Programme · 2 sessions | 2 hours each | Online / On-site | Planned |
| Emerging Standards Briefing — IEC TC62 Update | TBC 2027 | Briefing | 2 hours | Online | Planned |
| IEC 62304 Ed. 2 — Software Life Cycle Processes | TBC 2027 | TBC | TBC | Online / On-site | Planned |
| AI Validation for Life Sciences | TBC 2027 | TBC | TBC | Online / On-site | Planned |
Dates are indicative and subject to confirmation. to register interest or arrange bespoke in-house delivery.
Postgraduate Lecturing at DkIT
Alongside doctoral research, I lecture on one postgraduate module per term at Dundalk Institute of Technology at MSc Level 9 — covering healthcare software engineering, security, usability, and research practice.
Software Development and Validation in Healthcare
COMP_C9045 — Covering software development lifecycle processes and validation requirements for healthcare software, including IEC 62304 and regulatory compliance frameworks.
Further Modules
- Security in Healthcare
- Usability Engineering
- Research Methods
- Embedded Systems
- Healthcare Informatics
- Software Testing & Validation
- Medical Device Software Regulations
- AI in Healthcare
- Data Mining and AI
What Training Participants Say
Responses from a recent SaMD Software Development training programme, covering regulations, standards, software risk management, SOUP, and post-market surveillance.
“The trainer explanations and discussions were the most helpful part of the course — it was useful to all parts of my role, especially when focusing on clinical evidence generation.”
Julie Murdoc, Clinical
“The most valuable outcome was realising the importance of following regulations and being able to pass audits for the future of the company.”
Phillip Eccles, Technical
“This course grounds us and gives us the bigger picture, that we're not just shipping software, we're building a regulated medical device where the choices we make in code carry real clinical and patient safety implications. It's given me a much clearer sense of why the risk management, documentation and postmarket work actually matter, rather than feeling like box ticking, and how our day-to-day engineering decisions feed straight into that.”
Rona Clancy
Discuss a Training Programme for Your Team
Whether you are preparing your team for EU MDR compliance, building AI governance capability, or seeking an expert briefing on emerging standards, we welcome a conversation about how training can support your organisation.
Change Governance Maturity Assessment
How mature is your change governance?
Benchmark your organisation across 18 change governance domains, from regulatory change classification and risk to software release and AI/ML governance. Choose an 18-question quick check or a 91-question in-depth assessment, and get a maturity score, a radar chart, recommendations for each domain and a PDF report.
Free account required, so you can save results and track progress over time.
Launch the Assessment →AI-Enabled Tools for Lifesciences Compliance
Intelligent, trustworthy tools built on decades of regulatory and quality management experience — designed specifically for the lifesciences sector, with Human in the Loop review at every stage to meet regulatory expectations.
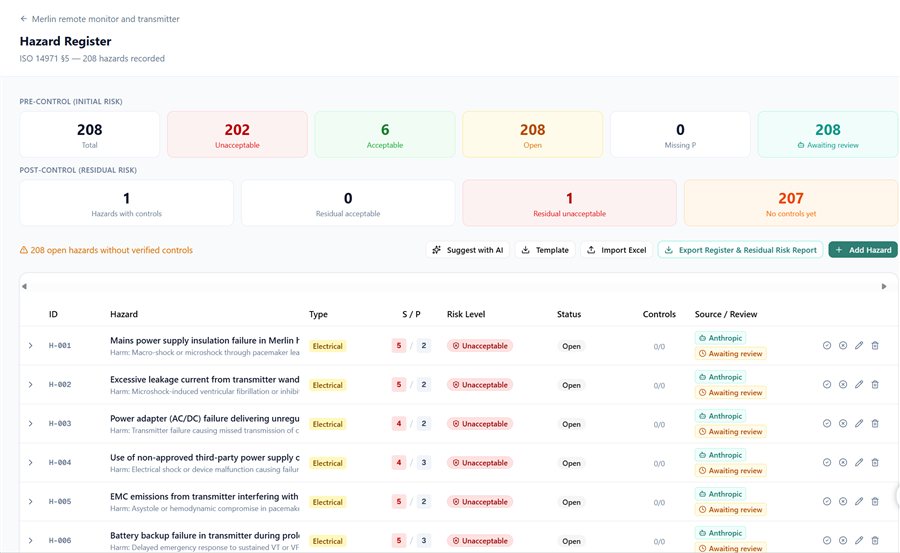
AskRiskie 2.0
An AI-enabled Risk Management Tool for Lifesciences organisations, designed for compliance with ISO 14971, ISO 27001, and associated standards. Trustworthy by design — with Human in the Loop review stages built to meet regulatory expectations across the full risk management lifecycle.
Register Interest →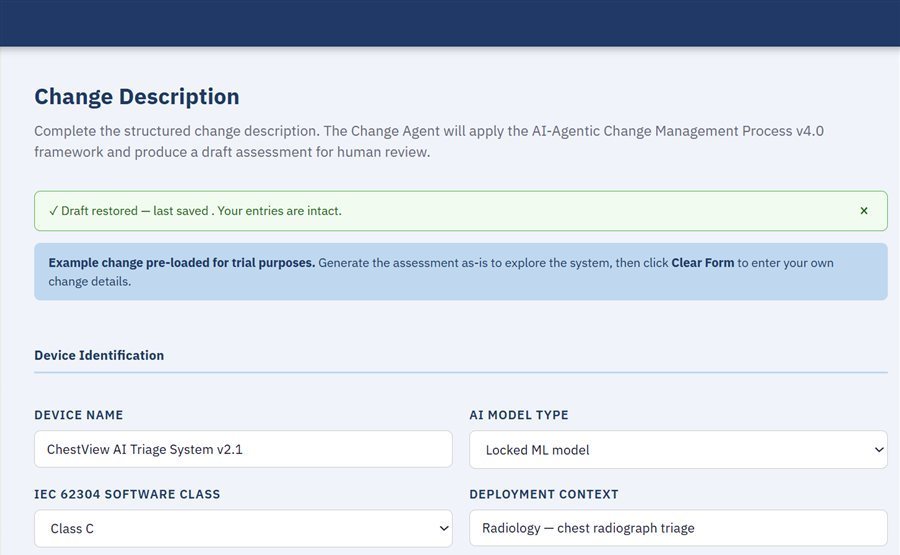
AIaCMP
The AI-agentic Change Management Process — an AI-enabled Change Assessment tool for Lifesciences under ISO 13485 and associated product standards and guidance. Trustworthy by design — with Human in the Loop reviews at key decision points to satisfy regulatory expectations.
Register Interest →Guides, Templates & Document Packs
Practical templates and SOPs for regulatory affairs, quality, and AI governance professionals working in medical devices. Some are free to download; others are available to purchase. All are developed from active research and industry practice. These are starting-point frameworks — if you need them tailored to your specific device, technology, or organisation, consulting support is available to adapt them to your context.
Software & AIeMD SOPs and Templates
Includes GenAI policy guidance (ISO/IEC TS 25568) — plus SOPs and templates for software and AI-enabled medical device development lifecycle under IEC 62304.
Note: content reflects IEC 62304 Ed.2 CD1 (first committee draft). Documents will be updated following CD2.
Software QMS SOPs & Templates
Quality Management System SOPs and templates for organisations developing medical device software, aligned to ISO 13485 and IEC 62304.
Note: content reflects IEC 62304 Ed.2 CD1 (first committee draft). Documents will be updated following CD2.
Opens in Payhip — our secure checkout
Cybersecurity & Security SOPs Pack
SOPs, templates, and work instructions for medical device cybersecurity, SBOM, incident response, and vulnerability disclosure.
Opens in Payhip — our secure checkout
Clinical Evaluation & PMS Pack
SOPs and templates covering clinical evaluation, PMCF, post-market surveillance, and vigilance reporting under EU MDR.
Opens in Payhip — our secure checkout
AI Governance Pack
Policy, validation, and change assessment documents for AI/ML governance in regulated medical device environments.
Pre-Trained AI Model Evaluation Pack
SOP, work instruction, and evaluation checklist for assessing pre-trained third-party AI models in medical devices and health software. Developed directly from peer-reviewed published research and the international standards work that followed — not generic templates, but documents that helped shape the emerging regulatory requirements in this space.
Opens in Payhip — our secure checkout
Usability Engineering & Human Factors Pack
SOPs, templates, and work instructions for usability engineering compliance under IEC 62366-1, integrated with ISO 14971 risk management. Includes an AI-specific usability assessment template and an AI Transparency & Explainability Evaluation Work Instruction — documentation not readily available elsewhere.
Opens in Payhip — our secure checkout
QMS Startup Pack — EU, UK & US
A complete Quality Management System foundation for new-start medical device organisations — Quality Manual, SOPs, templates, and work instructions aligned to ISO 13485 and applicable for EU MDR, UKCA, and FDA 21 CFR Part 820.
Opens in Payhip — our secure checkout
Gen-AI and MLMD Validation & Risk Analysis Pack
A complete set of tools for Validation and Risk Analysis of Generative AI and Machine Learning Medical Devices — SOPs, templates, and work instructions aligned to ISO 13485 and applicable for EU MDR, UKCA, and FDA 21 CFR Part 820. Given the absence of regulatory guidance, this pack provides practical frameworks for compliance.
Opens in Payhip — our secure checkout
Was This Useful?
Let us know how we're doing — your feedback helps improve the toolkit.
✓ Thank you — your feedback is appreciated!
Need Something Specific?
If you are looking for a resource tailored to your organisation's regulatory context — a bespoke checklist, gap analysis template, or training aide — get in touch to discuss what we can put together for you.
About St John Lynch & Co
Life Sciences Experts · Ireland & France
We are a life sciences consultancy bringing regulatory, quality, software, security and AI expertise to pharma, medical device, IVD and combination product organisations, from start-ups to global manufacturers. Our work is shaped by active research and by the standards committees where the rules are written.
Founded by Niamh St John Lynch
I founded St John Lynch & Co after 30 years in the life sciences. I began as a systems engineer and have worked across pharma, medical devices, IVDs and combination products, with companies including Novartis, Mylan (now Viatris) and Olympus, and spent four years as a Notified Body technical reviewer and site auditor. I have completed IRCA-certified Lead Auditor training in ISO 9001 and ISO 13485. I am registered for a doctorate at DkIT, under DCU, on trustworthy AI-enabled medical devices, and I chair NSAI/ETC/TC10 and contribute to IEC TC62 and CEN-CENELEC standards work.
Standards, Research & Education
Convenor of IEC 63767 ED1 - Evaluating 3rd Party Pre-Trained AI Models in Medical Devices
Expert Member, IEC TC62 — Plenary, AG SNAIG, ahG 11, JWG 12, JWG 15, PT 63450, PT 63621, SC 62A (incl. JWG 4 & MT 49 IEC 62304 Ed.2 Sub-Team Lead AI)
Member, CEN-CENELEC AI Task Groups 1 & 2
DkIT/UCD Collaborative Project on Trustworthy AI-enabled Medical Devices
Member, Regulatory Affairs Professionals Society (RAPS)
Member, ISPE GAMP Ireland
Publications & Profiles
In the Community
We aim to give up to 10% of our annual revenue to charity, with Focus Ireland and UNICEF among the causes we support most. Closer to home, we are proud to sponsor jerseys for St Colman's football club.
Talk to Us About Your Device
Whether you need a regulatory strategy, an audit, a development partner or training for your team, we would be glad to hear from you.
Work With Us
Open applications welcome
We work with experienced specialists in regulatory affairs, quality, software, security and AI for medical devices. If your expertise could help our clients, we would like to hear from you.
Areas We Work In
Our clients range from start-ups preparing a first submission to global manufacturers running complex programmes. We look for people with real depth in one or more of these areas.
Regulatory Affairs & Strategy
EU MDR/IVDR, UK, US and international market access, technical documentation and clinical evaluation.
Quality & Auditing
ISO 13485 and FDA QMSR quality systems, internal and supplier audits, and readiness reviews.
Software & AI Engineering
IEC 62304 and IEC 82304-1 software development, SaMD, and AI-enabled devices and automation.
Cybersecurity
IEC 81001-5-1 secure development, threat modelling, SBOM and vulnerability management.
Usability & Human Factors
IEC 62366-1 usability engineering, use-risk analysis and summative evaluation.
Training & Education
Designing and delivering training for industry teams in regulation, standards and AI.
Send Us Your Details
Email a CV and a short note on the areas you work in and the kind of projects you want to take on. We read every application and will be in touch if there is a good fit.
We use your details only to consider your application.
Get in Touch
We welcome enquiries about our services, doctoral research, standards development activities, or potential collaboration on regulatory science and AI governance in the medical device space. We are happy to discuss engagement opportunities with industry, regulators, or academia.
Book a free consult ↗
Where to Find Us
 Galway, Ireland
La
Tranche-sur-Mer, France
Galway, Ireland
St John Lynch & Co LtdDerrycallan North
Gort, Co. Galway
Ireland Open in map ↗